> For the complete documentation index, see [llms.txt](https://knowledgebase.autorabit.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://knowledgebase.autorabit.com/product-guides/arm-1/getting-started-1/arm-administration/user-management/enforce-single-sign-on-sso.md).
# Enforcing Single Sign-On (SSO)
Enforcing **Single Sign-On (SSO)** guarantees that every team member authenticates through your identity provider (IdP), enhancing security and simplifying password policies. Administrators can enable or selectively override SSO as needed.
***
## Enforce SSO for All Users
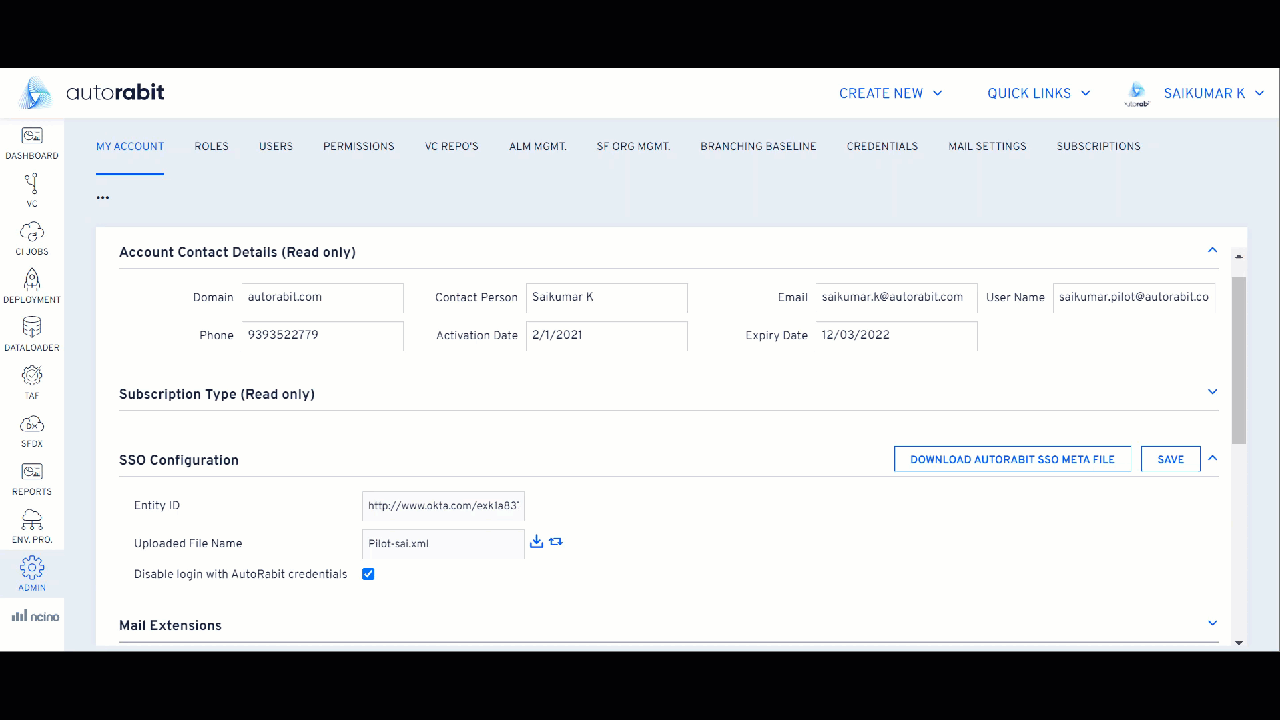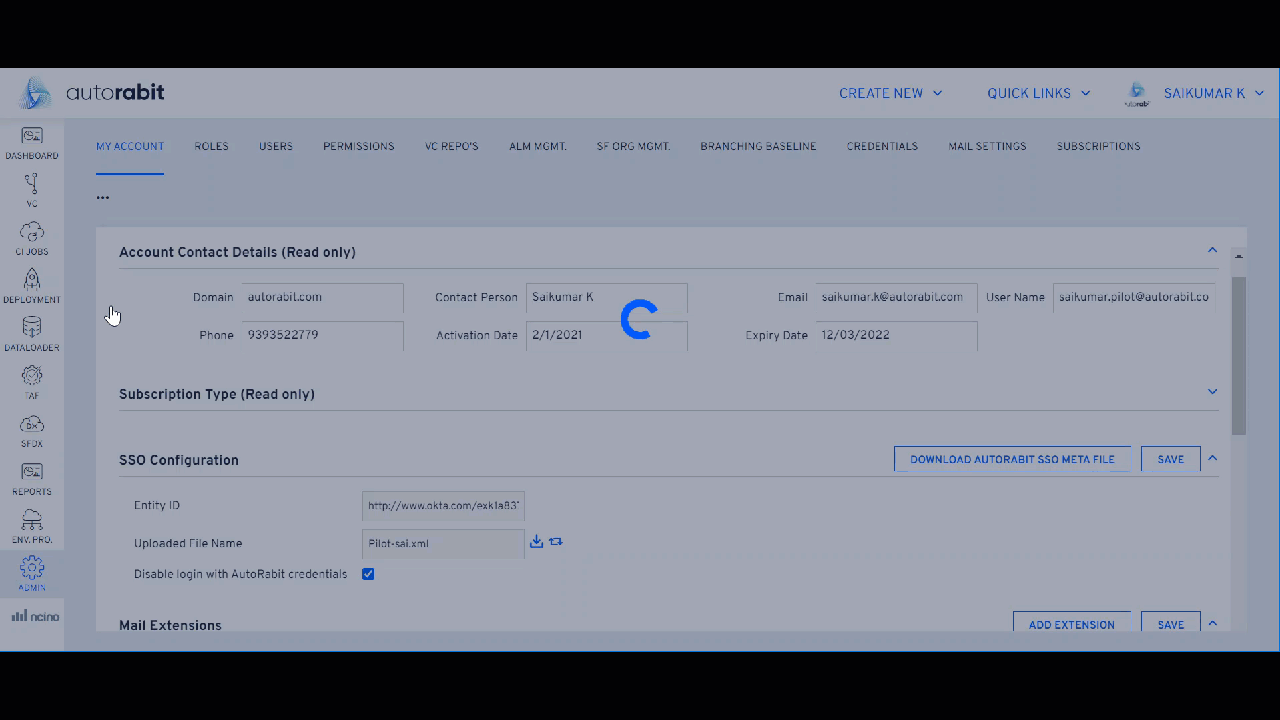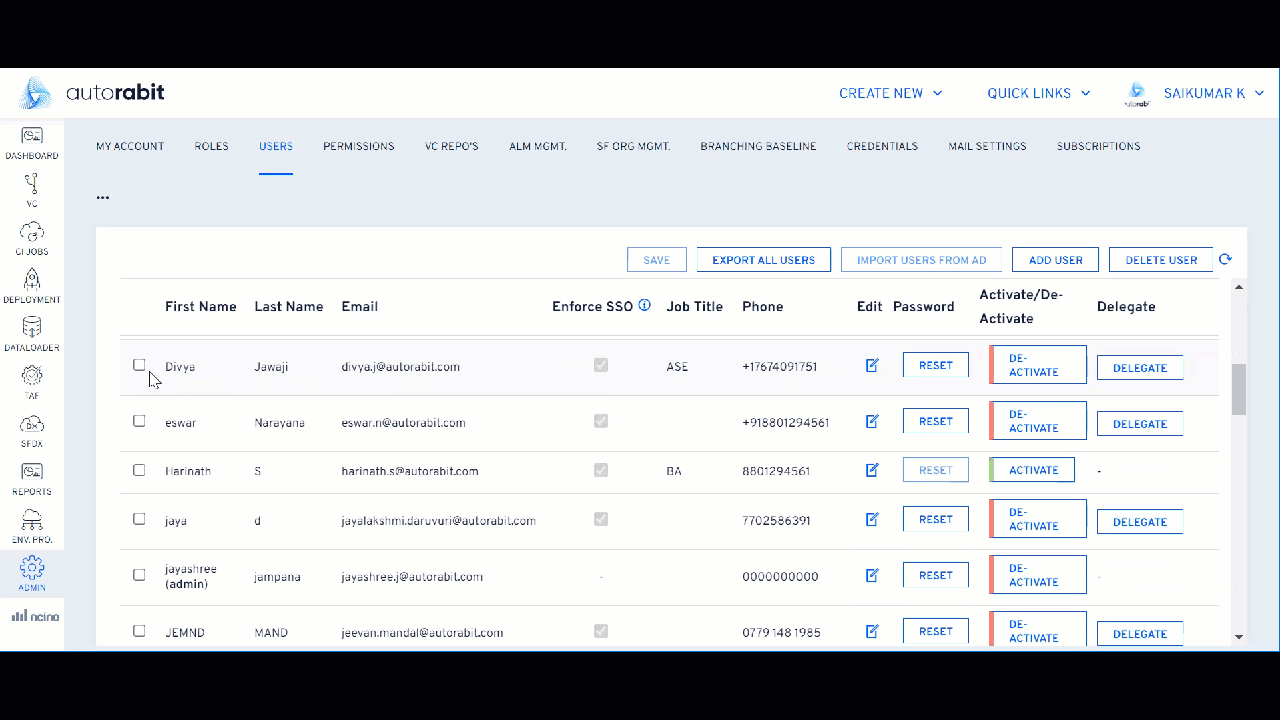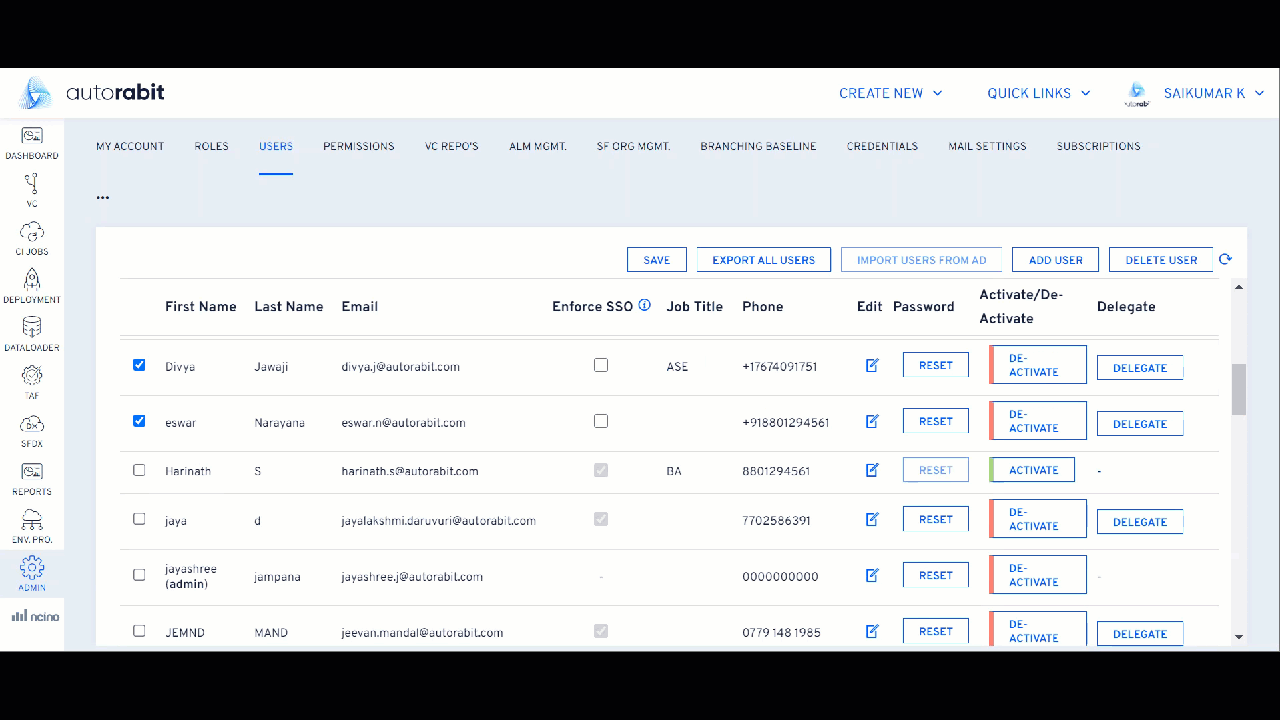
1. Open **My Account**.
2. In **SSO Configuration**, tick **Disable login with AutoRABIT credentials**.
3. Click **Save**.
From now on, all users must log in via SSO. Org Administrators can still sign in with either SSO **or** their AutoRABIT username/password—useful for IdP outages.
***
### Override SSO for Specific Users
An Org Admin can exempt individuals (e.g., contractors) from SSO without disabling it globally.
1. Go to **Admin › Users**.
2. Select the user(s) you want to exempt.
3. Untick the **Enforce SSO** checkbox next to their names.
4. Click **Save**.
{% hint style="info" %}
* Enabling **Disable login with AutoRABIT credentials** auto-checks **Enforce SSO** for every user.
* You can override on a per-user basis at any time.
{% endhint %}
## FAQ
### Does AutoRABIT support login IP restrictions?
Yes! Login IPs can be restricted via SSO. Previously, this was only possible with a dedicated, hosted instance. However, restrictions can be enforced via SSO using various providers.
- Here is a sample doc link from Okta on how to setup network zones that restrict access to apps registered in Okta.
- Likewise, here's one from Microsoft Entra SSO.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://knowledgebase.autorabit.com/product-guides/arm-1/getting-started-1/arm-administration/user-management/enforce-single-sign-on-sso.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.